Ukraine Ombudsman Data Protection Inspection: What Businesses Must Show
Reviews of our Clients
... our work on joint projects assured us of your high level of professionalism
Imagine this: the Commissioner's Secretariat contacts your company remotely and asks to see your personal data processing documents. You have a privacy policy on your website—and nothing else. A few weeks later, you receive an inspection report and compliance order: there is no internal procedure, no access log, and no one knows what to do in the event of a data breach.
A telling example is the scheduled remote inspection of a municipal enterprise reported by the Commissioner's Secretariat in March 2025. The inspection resulted in an inspection report and compliance order. The violations included the absence of an internal data processing document, inadequate notification of individuals, unregulated employee access, and the lack of a log of processing operations, a deletion procedure, and an incident response plan.
The problem is that most companies prepare for the wrong kind of inspection. They assume that collecting customer consent and posting a privacy policy on their website are what matter most.
A personal data inspection by the Ombudsman goes beyond checking for consent and a privacy policy. A business must show why and on what legal basis it processes each category of data, who has access, how processing operations are recorded, when data is deleted, and what the team does in the event of a data breach or loss of access.
This checklist is also useful for private businesses: it shows what evidence of compliance should exist in day-to-day operations, not just on paper.
Before reading further, try to answer honestly: do you know how many systems in your company store customers' personal data? If your answer is “I'm not sure,” this article is for you.
Why Consent Alone Is Not Enough
Consent is just one of the legal bases for processing under Article 11 of the Law of Ukraine “On Personal Data Protection.” A different legal basis may apply to HR records, contract performance, financial reporting, or compliance with another statutory obligation.
Collecting consent “for everything” is risky. If someone withdraws consent but the company actually needs to retain some of the data by law or to perform a contract, its internal documents will conflict with its actual processes. An audit should start by organizing processing activities by purpose and then identifying the appropriate legal basis for each operation.
For example, a single company may simultaneously process:
- employee data to formalize employment relationships and pay taxes;
- customer contact details to perform a contract;
- email addresses for promotional mailings;
- call recordings for quality control;
- video surveillance footage for office security.
These activities have different purposes and risks, and do not necessarily share the same legal basis.
Nine Questions to Ask Before an Inspection
1. Do You Have a Data Map?
A company must know what data it collects from employees, customers, job applicants, website visitors, and business partners. Each process needs to identify the data source, purpose, legal basis, storage location, users, recipients, and retention period.
Without a data map, a privacy policy almost always covers only the website, leaving out personnel files, the customer relationship management (CRM) system, accounting, video surveillance, cloud services, and backups.
For healthcare businesses, this data map becomes more complex because of an additional category: sensitive patient health data, discussed in the separate article “Sensitive Data in Healthcare and Its Protection.”
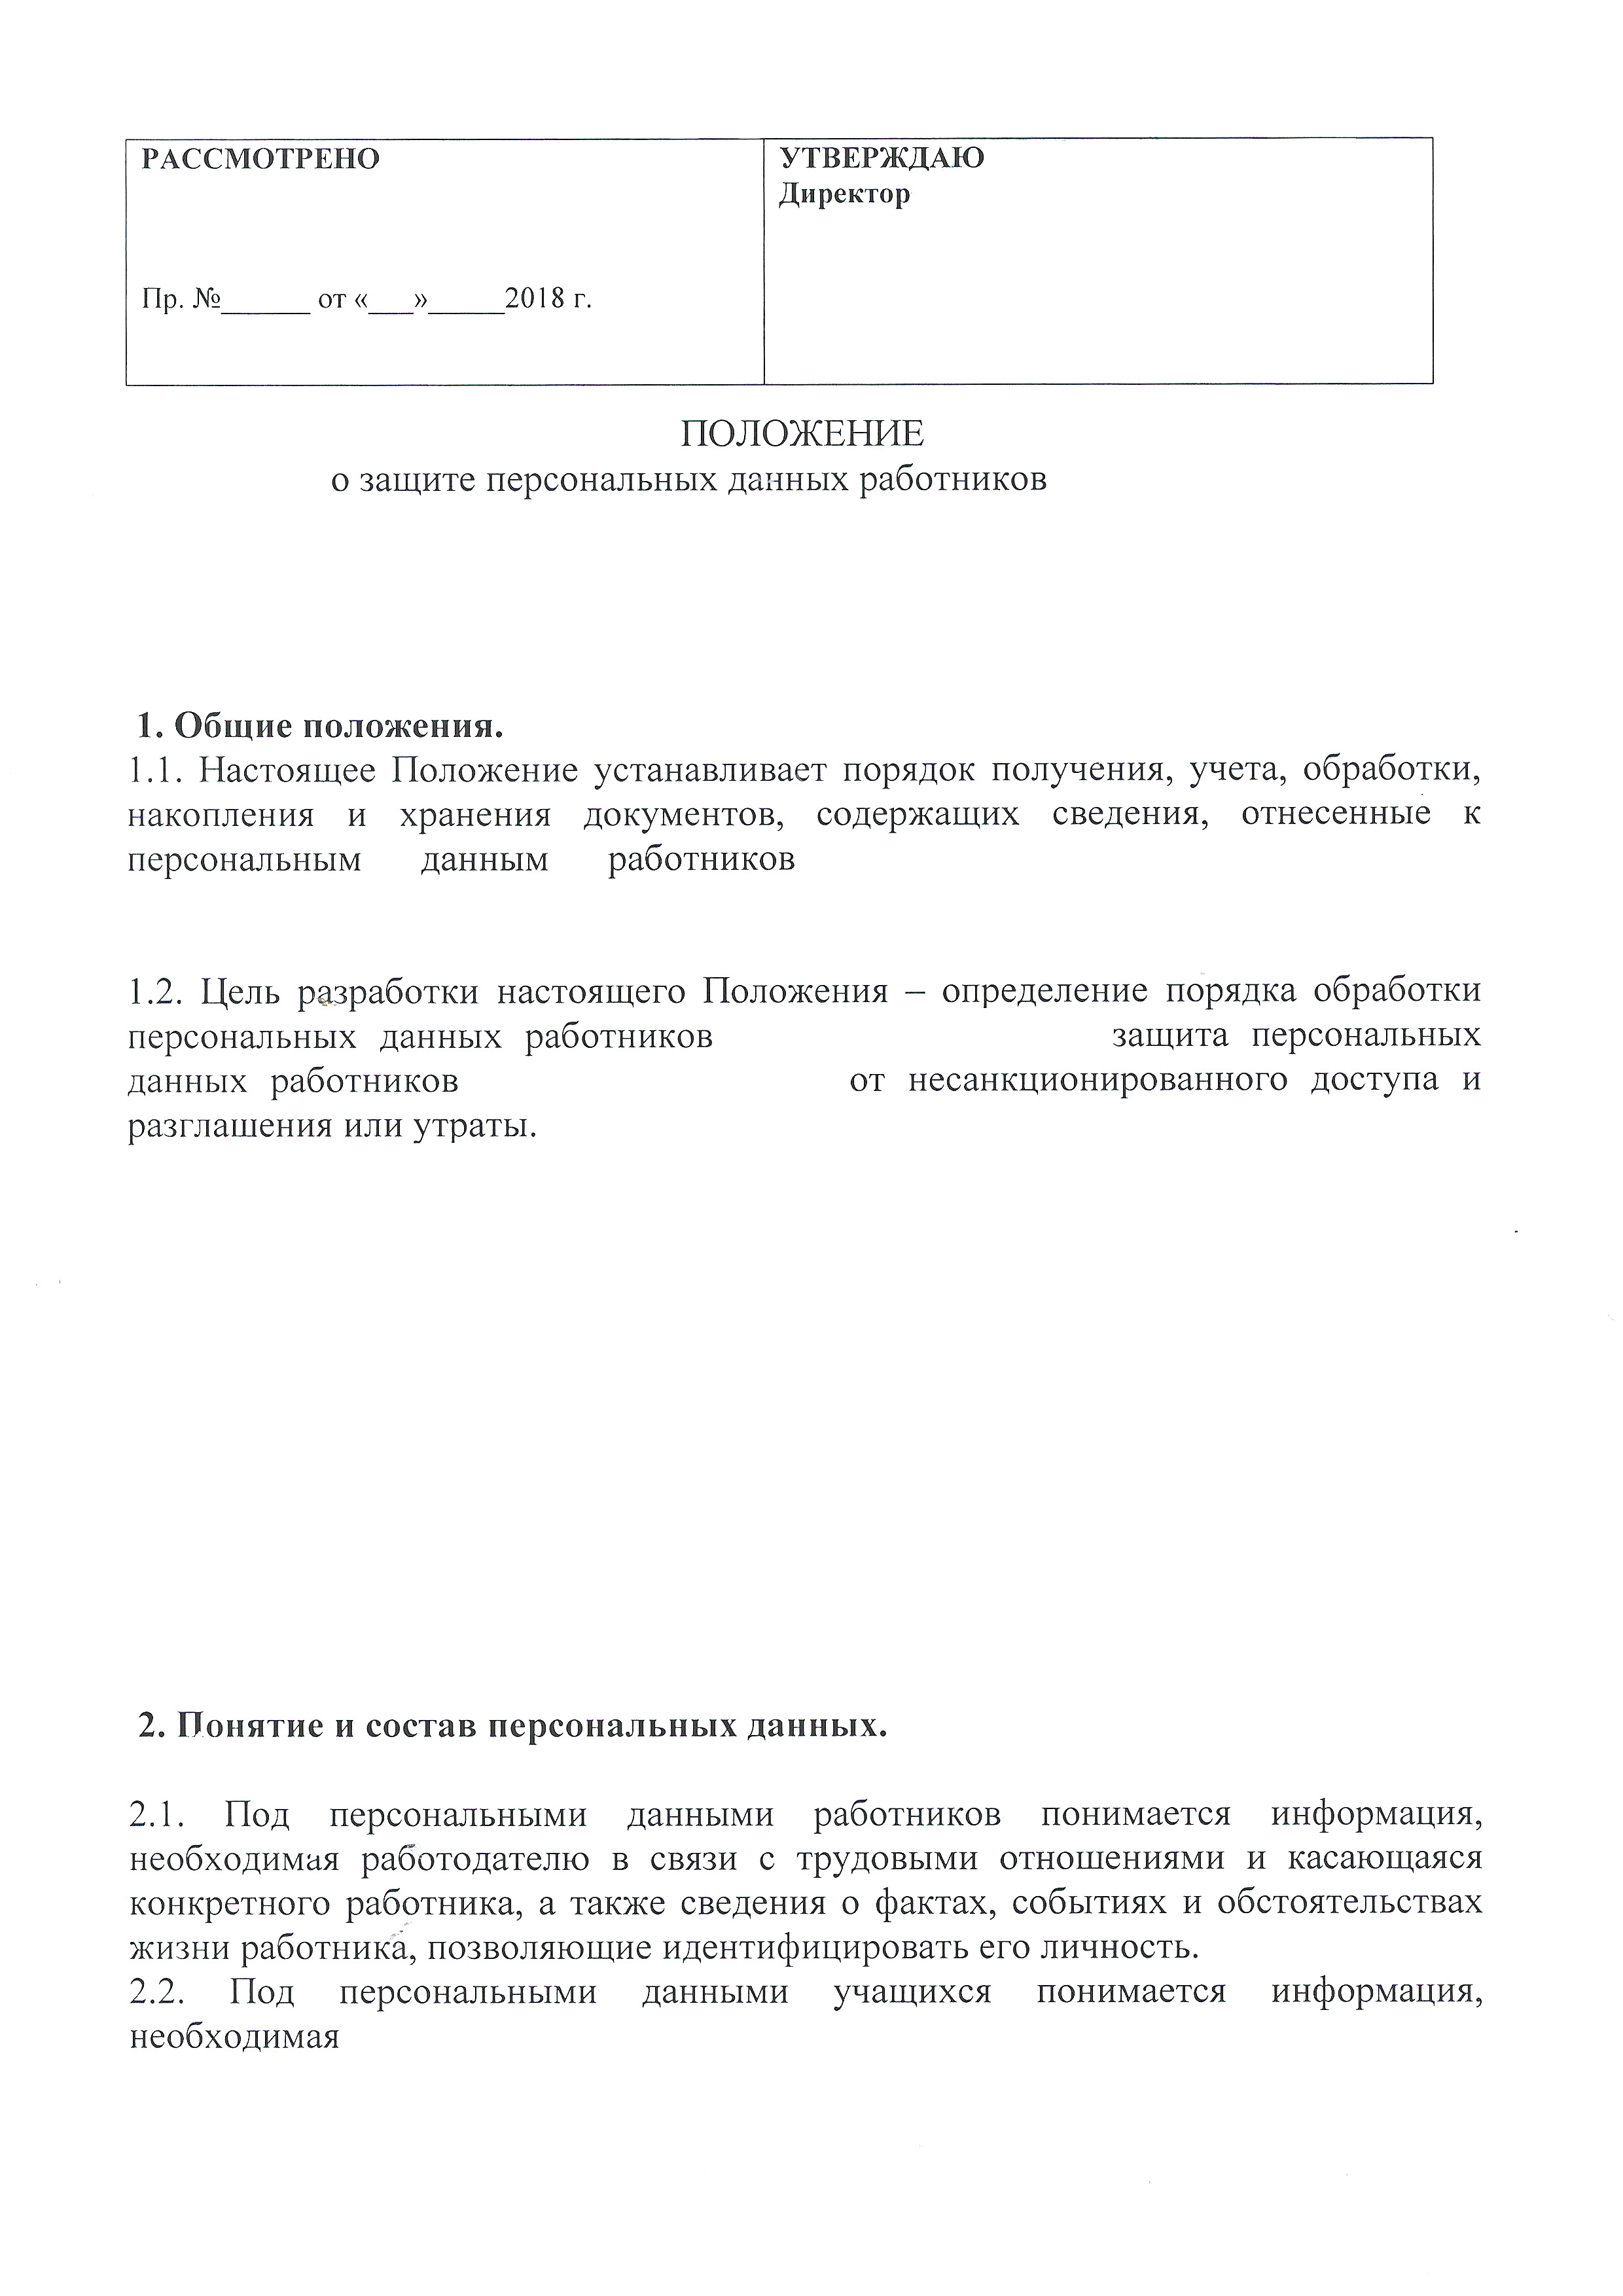
2. Has an Internal Data Processing Procedure Been Approved?
The Standard Procedure requires the controller to establish its own rules based on its activities. The document should describe specific categories of people and data, collection methods, transfers, access, retention periods, deletion, and security measures, rather than abstract principles.
If an internal document has been copied from another company, an inspection will quickly reveal discrepancies: it names one system while another is actually used; the policy omits a contractor that receives data; or a retention period is specified, but deletion has not been configured in the systems.
3. Do Individuals Receive a Privacy Notice?
Article 12 of the Law requires data subjects to be informed about the controller, the categories and content of the information collected, their rights, the purpose of collection, and the parties to whom the data is transferred. It is important to have both the text of the notice and evidence of when and how it was provided.
Different channels require different solutions: a notice in a job application form, HR documents, an order form, an app, or near an area under video surveillance.
4. Is Employee Access Restricted?
The 2025 inspection specifically identified the absence of an access procedure, records of employees with access, and differentiated access rights. Under an appropriate access model, an accountant sees the data needed for accounting, a manager sees their own customer's data, and an employee's access is revoked on the day of termination or a role change.
The list of authorized employees, their roles, and their written nondisclosure undertakings must match the actual system settings.
In our experience, this is often where documents and actual practices diverge: the policy limits access according to job responsibilities, but several employees actually share an account, and no one promptly revokes access for former employees.
5. Are Processing Operations Recorded?
The Standard Procedure provides for keeping records of the collection, modification, viewing, transfer, and deletion of personal data, as well as of the employee who performed each operation. This does not mean that every small company must buy a complex system. However, the recording method must work in practice, be proportionate to the risk, and make it possible to reconstruct events.
6. Are Contractors Monitored?
A CRM system, hosting provider, cloud drive, accounting service, call center, and advertising platform may receive personal data. The company needs to know exactly what is transferred to them, for what purpose, for how long, and what security measures and arrangements for returning or deleting data are included in the contract.
Saying “the contractor is responsible for security” does not eliminate the controller's risks.
7. Have Retention Periods and Deletion Deadlines Been Set?
The phrase “we retain data for as long as necessary” does not work without an internal retention schedule. The retention period must be linked to the purpose, the contract, and the requirements of employment, tax, accounting, archival, or other legislation. Once that period expires, the data must be deleted or destroyed in a way that prevents recovery, unless there is another lawful basis for retaining it.
Backups, email, and paper archives are checked separately: this is where “deleted” data often remains for years.
This is another common problem area. For example, a company sets retention periods in its documents but does not specify who must delete data from the CRM system, email, cloud storage, and backups, or how. As a result, the information is formally due for deletion but remains stored in several systems.
8. Is There a Procedure for Responding to Individuals' Requests?
An employee or customer may ask what data about them is being processed, request corrections, object to certain processing activities, or challenge unlawful actions. The team must know who receives the request, how the requester's identity is verified, where to look for information, and who approves the response.
Data must not be disclosed simply because an email bears the person's name: the requester's authority and the legal basis for the request must be verified first.
9. Is There an Incident Response Plan?
The Standard Procedure expressly calls for an action plan in the event of unauthorized access, equipment damage, or an emergency. A practical plan must specify whom employees notify, who stops the data breach, how evidence is preserved, how the scope of the incident is assessed, how operations are restored, and how decisions on external notifications are made.
The plan should be tested through a simulated incident. A document that the IT specialist, HR officer, and manager have never seen is unlikely to help during a real incident.
What to Present During a Remote Inspection
An off-site inspection is based on the documents and explanations submitted by the entity being inspected. The response should therefore include a consistent set of supporting evidence, rather than a single policy:
- an up-to-date internal procedure for data processing and protection;
- a map of processes and data categories;
- sample privacy notices for employees, customers, and other individuals;
- a list of roles with access and evidence of nondisclosure undertakings;
- rules for granting and revoking access;
- logs or other evidence of record-keeping of processing operations;
- retention periods and deletion records or technical evidence of deletion;
- contracts with key contractors;
- a procedure for handling requests and examples of responses without excessive disclosure;
- an incident response plan and evidence of employee training.
The documents must match the actual system settings. If the policy prohibits shared accounts but the sales department uses a single password, a formal set of documents will not protect the company.
Where to Start Your Internal Review
The first step is a brief assessment of what data the company holds, how it moves through the business, and which three gaps pose the greatest risk, rather than ordering a generic policy. You can then set priorities:
- revoke unnecessary access;
- improve privacy notices;
- approve deletion deadlines;
- review contractor agreements and train the team.
Contact us if you need a personal data processing audit, a risk map, internal and external documents, and support with implementing procedures in your company.
For more details, visit our service page: Personal Data Protection for Businesses.
This article reflects legislation and official guidance as of August 11, 2026.
Services on the topic of this material
Our publications on this matter
Our clients
We are ready to help you!
Contact us by mail [email protected] or by filling out the form:
Other publications by the author
The current age limit, automatic exclusion in the Register, steps if you were not excluded, and what happens to people excluded earlier and re-registered.
What TCC wanted status and the “Вас розшукує ТЦК” notice in Reserve+ mean, how to find the reason and six ways to remove the status, with pros, cons, timeframes and costs.
Cancellation of employee reservation ends the deferment of a reserved employee: who cancels it and when, the grounds under the Reservation Procedure, the steps in Diia, deadlines, what happens to the employee and the limit, and the employer's liability.
How to divorce a foreigner in Ukraine: when a joint application to the registry office is enough, when a court is needed, which court hears the case, what to do if the foreign spouse lives abroad, objects or cannot be found, and which documents to prepare.
Our other authors